

Cybersecurity in South Africa: Finding the Balance Between Cost, Risk, Resilience, and Regulation

South Africa has been navigating a tough economic landscape for some time. At the same time, it has become a prime target for cybercriminals, making cybersecurity a growing concern for enterprises across the country.
Beyond these economic and cyber pressures, IT and security teams are constantly battling operational challenges—outages, infrastructure issues, and the ever-present need for resilience and redundancy. These aren’t just best practices anymore—they’re essential requirements.
Adding to the complexity is the rising tide of regulatory obligations. This isn’t just about the fear of fines or the assumption that regulators are waiting to strike at the first sign of trouble. The real risk lies in what happens when your systems go down or are compromised. In those moments, everything changes with your key stake holders.
When a breach or outage occurs, your team must act fast to restore operations while external forensic teams are brought in to investigate. Meanwhile, you’re facing customers who want answers, trust that’s eroding, and regulators who now have every reason to scrutinize your business.
This is when the “we should have done more” realization hits. But often, the excuse is: “It’s economics.”
Very definitely, yes, cost is a factor! But risk mitigation doesn’t have to be a financial black hole. With a clear, cost-conscious strategy focused on “enough”—enough protection, enough compliance, enough readiness—you can dramatically reduce your exposure without breaking the bank.
So, where do you start?
Careful of using the big research & advisory firms! They can be helpful but many are paid by the vendors they mention….
Ask the right questions:
- ✅What cybersecurity solutions do we currently have in place?
- 💲What’s the annual cost, and where could we optimise?
- ❓Are there more affordable options that still meet our requirements?
- 👉What are we missing that would bring us closer to full compliance and stronger resilience?
Your “enough” checklist should include:
- 🔄 Reliable backup solutions
- 🔁 Redundant infrastructure to ensure uptime
- 🛡️ Endpoint Detection & Response (EDR)
- 🌐 Perimeter defense with SD-WAN
- 🔒 Micro-segmentation across hybrid environments
- 📊 SIEM, XDR, or SOAR for AI-driven security and log analysis
- 👥 Cybersecurity training for all employees
- 🔐 Multi-factor authentication (MFA)
- 🚫 Zero Trust Access controls
- 📈 Application performance monitoring
- 🕵️ Long-term monitoring for forensics, threat hunting, and post-incident analysis
Final Thought:
In today’s volatile environment, doing “enough” isn’t about perfection—it’s about being prepared. By taking a thoughtful, realistic approach to cybersecurity strategy, organisations can stay ahead of threats, maintain compliance, and protect both reputation and resilience—even when the pressure is on.

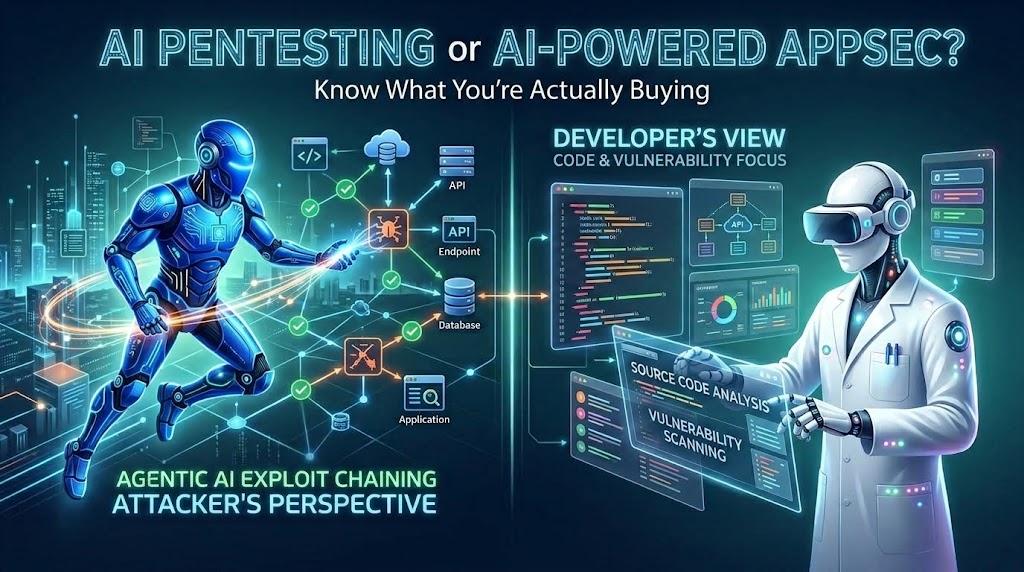
AI Pentesting or AI-Powered AppSec?
VendorKnow What You’re Actually Buying! By Hom Bahmanyar Ridge Security | Sep 29, 2026 |…
Observability- Evidence That Matters
VendorVIAVI News for NetSecOps Teams Moving from More Data to Better Decisions Modern investigations are no…
Introducing NetAlly “Ally Intelligence”
Bitrate NewsCollaboration-Powered Network Troubleshooting Now Available in South Africa & Sub-Sahara Africa The Next Evolution in…
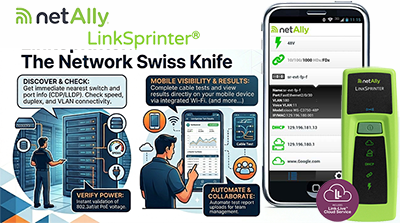
Network Test Swiss Army knife
Jeroen DubbelmanFocus on -Pocket size. Enterprise-level network testing. For Teams Requiring rapid resolution to network challenges…