Know What You’re Actually Buying!
By Hom Bahmanyar Ridge Security | Sep 29, 2026 | 11 min read
The security industry is entering a new era of AI-powered security testing.
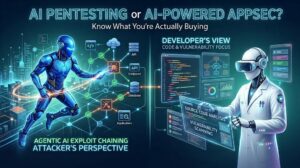
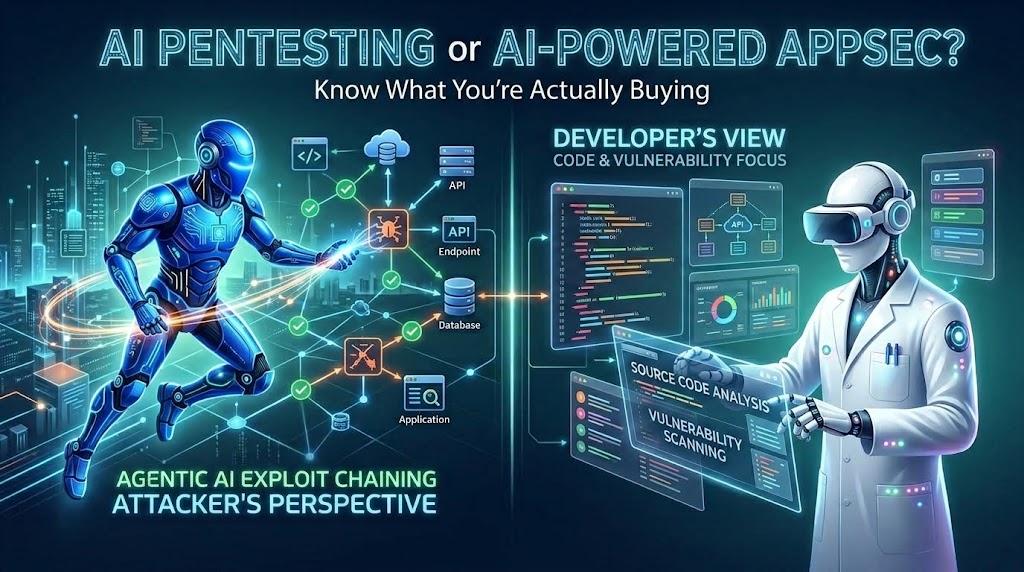
Agentic AI can reason through applications, identify vulnerabilities, generate exploits, adapt its approach, chain weaknesses together, and validate whether a vulnerability can actually be exploited.
But there’s a problem: the market is using “AI pentesting” to describe very different things. Some vendors apply AI to source-code analysis. Others automate web app testing. Few prove what an attacker can actually reach.
So the real question isn’t “Does it use AI?” It’s “Can it prove what an attacker can actually reach and exploit?”
In this post, you’ll learn:
- Why the code isn’t the environment: exposed services, missing patches, and misconfigurations that source-code scanning can’t see
- How real attacks chain: from web app to server to domain account to critical system
- Why CVSS doesn’t tell the whole story: reachability and attack paths matter more than severity scores
- White-box vs. black-box vs. gray-box: why you need all three
- 10 questions to ask any vendor claiming “AI pentesting”