

VIAVI Observer Threat Forensics, Now powered by CrowdStrike®
Modern Security Operations Centers (SOCs) are drowning in a sea of alerts, often hindered by fragmented visibility and a lack of deep context. To move from reactive to proactive, analysts need more than just signals—they need packet-level evidence and clear service-impact insights to respond with total confidence.
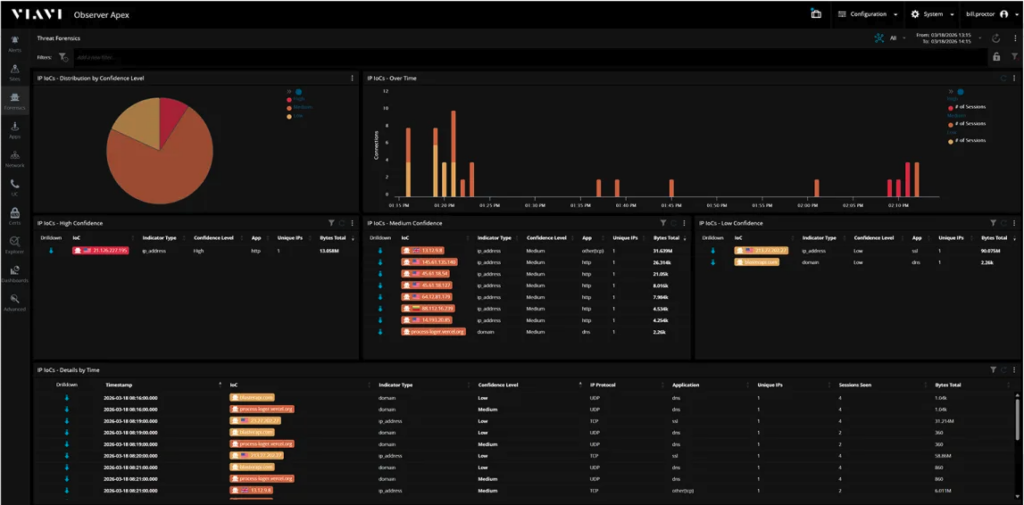
Observer Threat Forensics, bolstered by integrated threat intelligence powered by CrowdStrike®, bridges the gap between performance monitoring and advanced cybersecurity. By extending the trusted Observer platform, we empower NetSecOps teams to identify adversaries, reconstruct attack sequences, and collaborate using a single source of truth.
Where Threat Intelligence Meets Forensics
Observer Threat Forensics merges real-time intelligence with deep packet-level analysis. This synergy allows SecOps and NetOps teams to expose hidden risks and validate alerts with surgical precision, accelerating the journey from detection to remediation.
Key Capabilities for the Modern SOC
1. Real-Time Threat Intelligence Correlation
Detect with precision. Stop hunting for needles in haystacks. By continuously correlating live network traffic with dynamic threat intelligence, the system automatically identifies malicious behaviors, exploited vulnerabilities (CVEs), and attacker TTPs. Alerts are prioritized by impact, ensuring your team focuses on what matters most.
2. Forensic-Level Investigation
Validate threats with confidence. Every alert is more than just a notification—it’s a gateway. With direct links to packet-level evidence, analysts gain irrefutable visibility into the event. Reconstruct the entire attack sequence, from initial entry to lateral movement, to understand the true root cause and intent.
3. Comprehensive Visibility
See everything that matters. True security starts at the packet. By capturing both packet and flow data, Observer provides a 360-degree view of every device and communication path. This allows teams to uncover abnormal behaviors and “low and slow” threats before they disrupt critical business services.
4. Faster Mean Time to Respond (MTTR)
From alert to root cause in record time. Eliminate the “manual data stitch.” Automated correlation between packets and intelligence means that when suspicious activity is detected, the evidence is already waiting for you. This acceleration in validation and containment minimizes business disruption and limits the blast radius of an attack.
5. Retrospective Analysis
Rewind and uncover what was missed. Yesterday’s “normal” traffic could be today’s breach. With long-term metadata retention, you can perform retrospective detection on zero-day exploits. The solution automatically re-evaluates historical network activity to uncover persistent adversaries that may have initially evaded detection.
Past Blogs From VIAVI
NetOps + SecOps: The New Collaboration Model
The Data Behind NetSecOps Maturity – 2025/26 State of the Network Study
